
Palo Alto and Ivanti Zero-Days: Stolen Admin Logins and Tampered Logs Are This Week's Real Lesson
Table of Contents
- Introduction
- Palo Alto CVE-2026-0322: An Admin Login Becomes Root
- Who Is Affected and How to Fix It
- Ivanti CVE-2026-104935: No Login Needed at All
- The Attacker That Hid From Ivanti's Own Integrity Checker
- Lesson One: Admin Credentials Are Part of the Attack Surface
- Lesson Two: Don't Let a Device Grade Its Own Homework
- What to Do This Week
- Also Exploited This Month
- Building the Skillset Behind This at Innovative Academy
- FAQs
- Final Thoughts
1. Introduction
On October 13 and 14, 2026, two more network security products joined the list of devices being actively exploited: Palo Alto Networks' PAN-OS firewalls and Ivanti's Connect Secure VPN gateway. Both were added to the US Cybersecurity and Infrastructure Security Agency's (CISA) Known Exploited Vulnerabilities catalog.
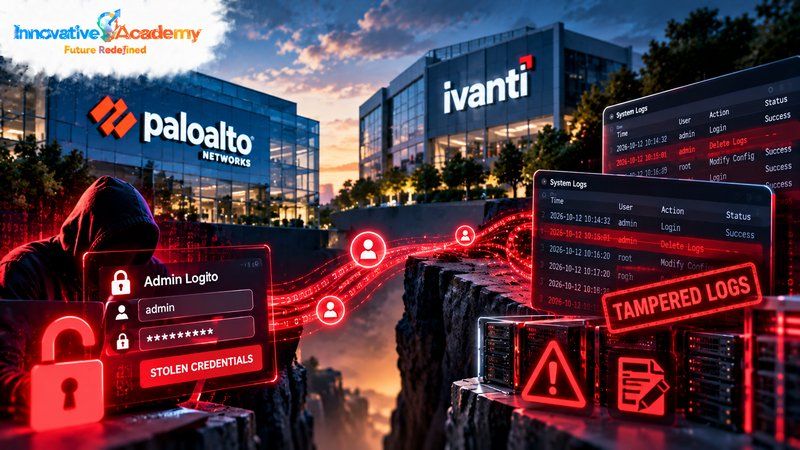
On the surface they are two separate advisories. Read together, they make two specific points that are easy to miss. The Palo Alto flaw shows that an admin password is only as safe as the device it unlocks. The Ivanti attack shows that a compromised device can be made to report that everything is fine.
2. Palo Alto CVE-2026-0322: An Admin Login Becomes Root
CVE-2026-0322 | CVSS 4.0 score 8.6 | Disclosed October 14, 2026
PAN-OS is the operating system that runs Palo Alto's firewalls. This flaw is a code injection weakness in the firewall's management interface, the web-based admin panel used to configure the device.
The catch is that it isn't open to just anyone. An attacker needs two things: valid high-privilege admin credentials and network access to the management interface. With both, they can run code as root, the deepest level of control over the firewall's underlying operating system. That is more power than even a legitimate administrator normally has through the admin panel.
Palo Alto says it has seen very limited exploitation. It found the flaw internally, and has not named the attackers or said how many organizations were targeted.
3. Who Is Affected and How to Fix It
- Affected: PA-Series and VM-Series firewalls and Panorama appliances running unpatched PAN-OS.
- Not affected: Cloud NGFW and Prisma Access.
- Fixed: Updates are available for PAN-OS 10.2, 11.1, 11.2, 12.1 and 12.2. The fix for the 11.2.16 line was scheduled for October 15. Use Palo Alto's advisory to find the exact build for your branch.
- Workaround: There is no full workaround. Palo Alto recommends restricting management interface access to trusted internal IP addresses and enabling the relevant Threat Prevention signatures.
- Indicators: Palo Alto published three IP addresses seen exploiting the flaw: 66.42.72[.]14, 208.83.239[.]114 and 149.248.47[.]234. Check your management interface logs for connections from them.
CISA has ordered US federal civilian agencies to mitigate the flaw by October 17.
4. Ivanti CVE-2026-104935: No Login Needed at All
CVE-2026-104935 | CVSS 8.6 | Disclosed October 13, 2026
Ivanti Connect Secure is an enterprise SSL VPN, the gateway remote employees and contractors use to reach internal company systems. This flaw is an authentication bypass: by spoofing part of the login process, a remote attacker with no credentials at all can get past the login check and execute arbitrary commands on the appliance.
Ivanti says the flaw was exploited against a limited number of customers before it was disclosed. Security firm Volexity, which investigated the attacks, says a threat actor it tracks as UTA0576 has been exploiting it since at least October 3. Another firm, Defused, saw the first signs of exploitation on October 1.
- Fixed: Ivanti has released updates. Affected and fixed versions differ by release branch, and early reports list them differently, so check Ivanti's own advisory for your version. Ivanti says version 22.7R2.14 and earlier are not affected.
- Not fully closed: The attackers chained this flaw with a privilege escalation vulnerability that Ivanti has not yet patched. Patching CVE-2026-104935 is necessary, but it isn't the end of this story.
CISA added the flaw to its catalog the same day it was disclosed and gave federal agencies until October 16 to fix it.
5. The Attacker That Hid From Ivanti's Own Integrity Checker
The most instructive detail in the Ivanti case isn't the flaw itself. It's how the attacker stayed hidden.
Ivanti provides an Integrity Checker Tool that administrators can run to see whether their appliance has been tampered with. According to Volexity, this attacker avoided leaving anything persistent behind for that tool to find. Instead of installing a backdoor, it re-exploited the device every time it wanted to run a command, and it tampered with logs to cover its tracks. The result was a compromised appliance that could pass the vendor's own health check.
Ivanti has been here before. CISA has flagged 36 vulnerabilities across Ivanti products as actively exploited since November 2021, 12 of which ransomware gangs have also used.
6. Lesson One: Admin Credentials Are Part of the Attack Surface
It's tempting to file the Palo Alto flaw as low-risk because it needs a login. That reasoning has two problems.
First, admin credentials leak all the time: reused passwords, phishing, credentials stolen from an earlier breach, or a former employee's account that was never disabled. Second, this flaw changes what a stolen login is worth. Without it, an attacker with admin access can change firewall rules. With it, they can take over the device's operating system, which is far harder to detect and undo.
The practical takeaways are straightforward:
- Keep the management interface off the internet. It should only be reachable from a dedicated management network or a small set of trusted internal addresses.
- Use multi-factor authentication for every admin account that supports it.
- Keep the admin list short and review it regularly. Remove accounts that are no longer needed.
- Use unique admin passwords that aren't shared with any other system.
None of these fix the flaw, but they make the credential the attacker needs much harder to get and use.
7. Lesson Two: Don't Let a Device Grade Its Own Homework
The Ivanti case is a clear example of a principle that applies to every network appliance: once an attacker controls a device, anything that device reports about itself can be falsified. Its logs, its status pages and even its vendor's integrity tools all run on the compromised system.
That's why the most reliable evidence comes from outside the device. In practice, that means:
- Send logs off the device to a central syslog server or SIEM as they're generated, so an attacker can't quietly rewrite history.
- Watch the device's traffic from the network, using flow data from the switches and routers around it, for connections it shouldn't be making.
- Treat a clean integrity check as one data point, not a final verdict.
8. What to Do This Week
- Find out if you run either product. List every Palo Alto firewall, Panorama appliance and Ivanti Connect Secure gateway, with exact software versions.
- Patch both flaws now. Use the vendor advisories to match your exact version to its fixed build.
- Lock down management access. Confirm the PAN-OS management interface isn't reachable from the internet.
- Check for the published indicators. Search firewall and management logs for the three IP addresses Palo Alto shared.
- Review Ivanti gateways beyond the integrity check. Look at network traffic from outside the appliance for unusual activity since October 1.
- Watch for Ivanti's second patch. Apply the privilege escalation fix as soon as Ivanti releases it.
9. Also Exploited This Month
Palo Alto and Ivanti weren't the only security appliances under attack in early October. We've covered the others in separate posts:
- Cisco's Email Gateway Zero-Day Is Under Attack — and the Fix Had Already Shipped a Month Earlier
- A Critical FortiMail Flaw Is Being Exploited Right Now
10. Building the Skillset Behind This at Innovative Academy
Innovative Academy's Hardware & Networking program in Bangalore, which covers CCNA and CCNP-aligned networking and security fundamentals, teaches the concepts at the heart of both lessons in this post: separating management traffic from user traffic, controlling and authenticating administrative access, and setting up syslog and network monitoring so the evidence about a device doesn't depend on the device itself.
11. FAQs
1. Can the Palo Alto flaw be exploited without a password?
No. CVE-2026-0322 requires high-privilege admin credentials and network access to the PAN-OS management interface. That's why keeping the management interface off the internet and protecting admin accounts matters so much.
2. Is this the same Palo Alto zero-day that was exploited in May?
No. In May, attackers exploited CVE-2026-0300, a different flaw in the firewall's captive portal that needed no login. CVE-2026-0322 is a new flaw in the management interface that requires admin credentials.
3. Does the Ivanti flaw need a login?
No. CVE-2026-104935 is an authentication bypass, so a remote attacker with no credentials can run commands on a vulnerable gateway.
4. Is patching Ivanti enough?
Not yet. Ivanti has patched the authentication bypass, but the attackers also used a privilege escalation flaw that Ivanti is still working to fix. Apply that patch when it's released, and check gateways for signs of compromise in the meantime.
5. If Ivanti's Integrity Checker Tool says my gateway is clean, am I safe?
Not necessarily. Volexity reports that this attacker evaded the tool by not leaving persistent changes and by tampering with logs. Review network traffic and centrally stored logs from outside the appliance as well.
12. Final Thoughts
These two advisories land in the same week, but they teach different things. Palo Alto's flaw is a reminder that admin access is a security boundary in its own right, and that a stolen login can be worth far more than it looks. Ivanti's attack is a reminder that a compromised device can't be trusted to report on itself. The teams best placed for the next advisory are the ones that keep management interfaces locked away, protect admin accounts like the keys they are, and collect their evidence from outside the devices they're trying to verify.
Innovative Academy — Contact for course details: 8447712333
Website · Facebook · Instagram
Sources:
- BleepingComputer — Palo Alto Networks Warns of PAN-OS RCE Flaw Exploited in Attacks
- SecurityOnline — Palo Alto PAN-OS RCE Vulnerability CVE-2026-0322 Actively Exploited
- BleepingComputer — Ivanti Warns of Connect Secure Zero-Day Exploited in Attacks
- Rapid7 — Ivanti Connect Secure Zero-Day Exploited in the Wild
- Innovative Academy — Hardware & Networking Course in Bangalore