
Table of Contents
- Introduction
- What CVE-2026-76519 Actually Does
- The Two Conditions That Make a Gateway Vulnerable
- Why the Fix Was Already Out Before Anyone Knew It Mattered
- How to Fix It
- How to Check Whether a Gateway Was Already Hit
- If a Gateway Is Compromised
- The Third Root-Level Flaw Exploited in These Appliances Since December
- Building the Skillset Behind This at Innovative Academy
- FAQs
- Final Thoughts
1. Introduction
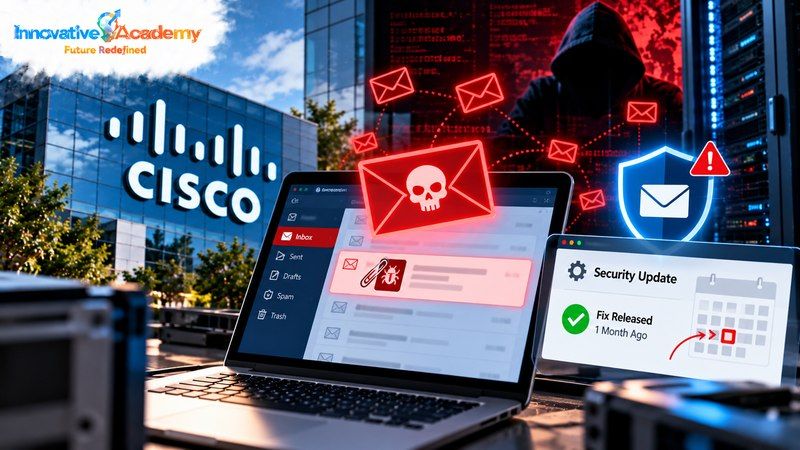
On October 14, 2026, Cisco warned that attackers are actively exploiting a critical vulnerability in Cisco Secure Email Gateway, the appliance many organizations place in front of their mail servers to filter spam, malware, and phishing. The flaw, tracked as CVE-2026-76519, carries a CVSS score of 9.8. The unusual part of this story is not the severity. It's the timing: the fix had already been shipping for a month, inside a routine hardening release that most administrators would have had little reason to treat as urgent.
2. What CVE-2026-76519 Actually Does
The attack starts with an email. An attacker sends a message carrying a specially crafted attachment through the gateway. No login is required. If the attack succeeds, the attacker can write files to the appliance's underlying operating system, and from there could run commands as root, the highest level of control on the device.
That matters because of where an email gateway sits. It processes every inbound and outbound message for an organization, so root access on it puts an attacker inside a device that sees a large share of the company's communications. Cisco found the flaw through its own internal security scanning and became aware of attacks in October. Its advisory does not say how many devices were attacked, who is behind the attacks, or whether attackers actually reached root on any of them.
3. The Two Conditions That Make a Gateway Vulnerable
Not every Secure Email Gateway is exposed. Both of these must be true at the same time:
- File Reputation is enabled and assigned to a mail policy. File Reputation is part of Cisco's Advanced Malware Protection (AMP) feature, which inspects attachments.
- The Content Scanner Tools package is older than version 25.3.0.5525.
Both physical and virtual gateways on vulnerable AsyncOS releases are affected. Cisco's Secure Email and Web Manager and Secure Web Appliance are not.
To check the first condition, go to Mail Policies > Incoming Mail Policies > Advanced Malware Protection (and the same path under Outgoing Mail Policies), select each mail policy, and look at the Enable File Reputation setting. To check the second, run contentscannerstatus at the command line, which shows the installed version and when it was last updated.
4. Why the Fix Was Already Out Before Anyone Knew It Mattered
On September 14, Cisco published a hardening release for the gateway. Under a disclosure policy Cisco introduced in June, bugs found internally and fixed in hardening releases are grouped into a handful of umbrella CVEs by weakness type, rather than each getting its own advisory. That September release grouped its fixes into five umbrella CVEs, four of them rated 9.8.
The file-write flaw was one of the bugs quietly fixed inside that release, filed under the path traversal group. Under Cisco's policy, a bug gets its own CVE and advisory when, among other reasons, it is known to be exploited. Once Cisco saw attacks in October, CVE-2026-76519 was split out and announced on its own.
The practical lesson is uncomfortable but useful: a hardening release can contain a critical fix that won't be publicly identified as critical until after attackers find it. Organizations that applied the September release promptly were protected weeks before this advisory existed. Organizations that deferred it because it looked like routine maintenance were not.
5. How to Fix It
There is no workaround. The fastest route is the scanner update, which installs without a full software upgrade or a restart:
- Content Scanner Tools 25.3.0.5525 or later: If automatic scanner updates are on, the update should apply on its own, but confirm the version with
contentscannerstatusrather than assuming it arrived. If automatic updates are off, runcontentscannerupdateat the CLI, or enable them under Security Services > Service Updates.
The full AsyncOS fix is in these releases:
- AsyncOS 15.5: 15.5.5-014
- AsyncOS 16.0: no fixed build. Migrate to a fixed release.
- AsyncOS 16.5: 16.5.0-780
Cisco recommends that any gateway earlier than 16.5 move to 16.5.0-780. One trap to watch for: a 16.0 gateway running 16.0.4-302, the build that fixed September's separate SQL injection flaw, is not fixed for this one. For a gateway staying on 16.0, the Content Scanner Tools version is the only confirmation Cisco's advisory offers.
Customers of Cisco's managed Secure Email Cloud service don't need to act to get the fix; Cisco has already deployed the updated scanner there and has contacted customers whose devices showed indicators of possible compromise.
6. How to Check Whether a Gateway Was Already Hit
Patching closes the door, but it doesn't tell you whether someone already walked through it. Cisco's check is a single command on the appliance:
grep "System Security" system_logs
It returns one of three results: a suspected compromise indicator was found, the security scan did not complete, or no compromise indicator was found. The first two mean contacting Cisco's Technical Assistance Center (TAC).
Two important caveats. First, run the check on every member of a cluster, not just one. Second, a clean result is not proof. An attacker with root access could remove or hide evidence on the device itself, so it's also worth reviewing firewall and network logs outside the appliance for unexpected uploads to external IP addresses or downloads from suspicious ones.
7. If a Gateway Is Compromised
For a physical appliance, Cisco asks customers to contact TAC and enable remote access so its engineers can investigate. For a virtual appliance, the recovery steps are:
- Preserve forensic data first. Upgrading a compromised instance destroys its logs and evidence.
- Deploy a new virtual machine on a fixed release.
- Rebuild the configuration from scratch, without importing any previous configuration file.
- Renew all credentials and cryptographic material, then keep monitoring for unusual behavior.
Clusters need extra care. Cluster members authenticate to each other using SSH key pairs, so a compromised member's private keys could give an attacker a path into the others. Cisco recommends restoring every member of a cluster that contains even one compromised appliance.
8. The Third Root-Level Flaw Exploited in These Appliances Since December
This is not an isolated incident. It's the second Secure Email Gateway flaw Cisco has confirmed under attack in about a month. On September 14, Cisco disclosed CVE-2026-76461, a SQL injection flaw in the gateway's email parsing that could also let an unauthenticated sender run commands as root. That one affects every configuration and was added to CISA's Known Exploited Vulnerabilities catalog the same day. Cisco has not linked the two sets of attacks.
Before that, in December 2025, a China-linked group that Cisco Talos tracks as UAT-9686 exploited a zero-day in the appliance's spam quarantine feature (CVE-2025-20393), which Cisco patched in January. Three root-level flaws exploited in under a year makes the email gateway a clearly established target, not an occasional one.
9. Building the Skillset Behind This at Innovative Academy
Innovative Academy's Hardware & Networking program in Bangalore, which covers CCNA and CCNP-aligned networking and security fundamentals, builds the practical habits this advisory rewards: knowing where a security appliance sits in the network, reading a vendor advisory for the exact conditions that make a device vulnerable, working confidently at the command line, and treating a clean log check as one data point rather than a final answer.
10. FAQs
1. Is every Cisco Secure Email Gateway vulnerable to CVE-2026-76519?
No. A gateway is only vulnerable if File Reputation is enabled and assigned to a mail policy, and its Content Scanner Tools version is older than 25.3.0.5525. Secure Email and Web Manager and Secure Web Appliance are not affected.
2. Does the attacker need a password or account?
No. The attack works by sending an email with a crafted attachment through the gateway, with no login required.
3. What's the quickest way to fix it?
Update Content Scanner Tools to version 25.3.0.5525 or later, which doesn't require a software upgrade or restart, then confirm the version with the contentscannerstatus command. For the full fix, move to AsyncOS 15.5.5-014 or 16.5.0-780.
4. Is there a workaround if I can't patch right away?
Cisco says there is no workaround. Applying the scanner update is the fastest available fix.
5. If my compromise check comes back clean, am I safe?
Not necessarily. An attacker with root access could hide evidence on the device. Cisco advises also checking firewall and network logs outside the appliance for unexpected traffic to or from external IP addresses.
11. Final Thoughts
The headline here is a 9.8-rated zero-day, but the more lasting lesson is about patch habits. Cisco's fix for CVE-2026-76519 was available a full month before the advisory, bundled in a hardening release that didn't call it out by name. The organizations that were safe weren't the ones who reacted fastest to this week's news. They were the ones who already treated security appliance updates as routine work to apply promptly, rather than something to defer until a scary CVE number shows up.
Innovative Academy — Contact for course details: 8447712333
Website · Facebook · Instagram
Sources: