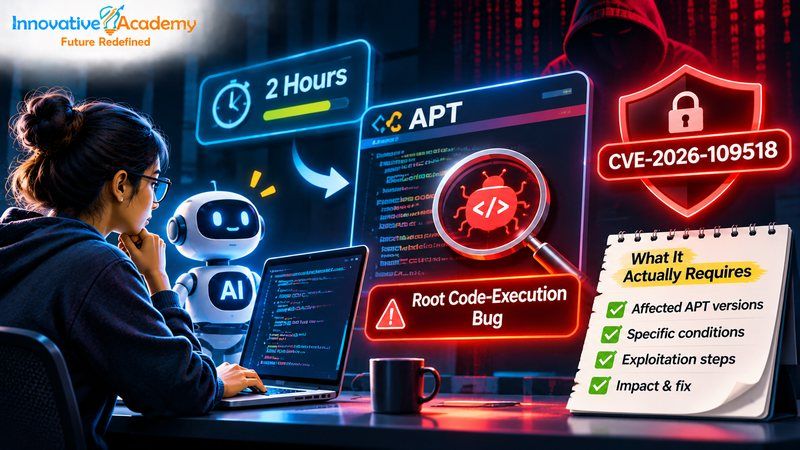

A Researcher Spent Two Hours With an AI Tool and Found a Root Code-Execution Bug in APT — Here's What CVE-2026-109518 Actually Requires
Table of Contents
- What's confirmed, and who found it
- A few terms worth defining before the mechanism
- How the substitution actually works
- Why one configuration setting decides whether you're exposed at all
- The fix, and what to do if you can't patch today
- Why this is a fundamentals story for Linux administrators
- What we're not claiming
A researcher's own description of this bug is the kind of quote that gets a vulnerability shared well beyond the usual security press: "I used an AI for two hours and found a zero-day that would let a nation-state hack any server running stock Ubuntu." That's Max Justicz, in a public post about CVE-2026-109518, a flaw in APT — the package manager underneath Debian, Ubuntu, and most of their derivatives. The underlying bug is real and now patched. The headline framing, as is often the case, compresses away a precondition that matters a lot in practice. Here's what the advisories and the reporting on them actually establish, separated from the one-liner that made this story travel.
What's confirmed, and who found it
Debian disclosed the flaw on November 4, 2026, crediting independent researcher Max Justicz, with CSO Online's Shweta Sharma covering it the following day. Debian issued Security Advisory DSA-6607-1 for Trixie and DLA-4880-1 for Bookworm's long-term support branch; Debian's own security tracker lists CVE-2026-109518 against the apt source package directly. Ubuntu rated the issue High severity with a CVSS score of 7.7 and shipped fixes the same day as Debian's disclosure. Justicz's "zero-day" framing in his own post is his personal description, not a formal classification from either vendor's advisory — worth keeping in mind as a separate thing from the technical facts below.
A few terms worth defining before the mechanism
APT (Advanced Package Tool) is the software that downloads, verifies, and installs packages on Debian, Ubuntu, and most of their derivatives. Because installing a package typically requires root privileges, a flaw that lets APT install something other than what it verified effectively hands an attacker root-level code execution.
An on-path attacker sits somewhere on the network between your machine and the package mirror it's downloading from — a compromised proxy, a malicious mirror, or anyone with that kind of positioning — and can alter traffic passing through. This is a meaningfully narrower attacker model than "anyone on the internet": it requires actual network positioning, not just knowledge of a target's IP address.
A hard link, at the filesystem level, is a second name pointing at the exact same underlying file data — not a copy. If something rewrites the data behind one hard link, every other name pointing at that same data reflects the change instantly, because there's only ever been one file, just reached by two different names.
How the substitution actually works
Based on Debian's advisory and tracker entry, the root cause sits in how APT handles two specific, ordinary situations together: HTTP redirects and retried, resumed downloads. APT can end up treating two genuinely different downloads as the same object when an HTTP redirect causes both to resolve to an identical URI. Separately, when a download gets interrupted and APT retries it, the resumption logic can end up reusing an existing hard link tied to that partially-downloaded file rather than starting fresh. Put those two behaviors together and an attacker positioned on the network path — able to trigger a redirect and manipulate the retried response — can get their own payload substituted in through that reused hard link, after APT has already verified the package it thought it was downloading. No forged GPG signature is needed, because the substitution is a file-handling trick that happens around the verification step, not an attack on the cryptography itself. Debian's description attributes the whole mechanism to this hard-link reuse rather than to any flaw in APT's signature-checking logic — the signing chain itself isn't what's broken here.
Why one configuration setting decides whether you're exposed at all
The single detail that matters most for figuring out your own exposure is a setting called Acquire::Retries. The vulnerable behavior only triggers when this value is nonzero — meaning APT is configured to automatically retry a failed or interrupted download rather than simply giving up. Per Debian's tracker entry, a default retry value of three has been in place since Debian 12 (Bookworm) and Ubuntu 22.04 LTS; releases older than that aren't exposed by default, though an administrator who explicitly turned retries on for an older system would still be affected. That default is also exactly why this reached so many systems at once without anyone having changed a setting — most Debian and Ubuntu installations from the last several years simply inherited it.
The fix, and what to do if you can't patch today
APT developer Julian Andres Klode's fix, committed October 12, changes the download code to open destination files exclusively and unlink any existing file before writing partial content to it — closing off the path that let an existing hard link get silently overwritten. That the fix predates the public disclosure by roughly three weeks is a reasonable sign this followed something closer to coordinated disclosure practice than an emergency scramble after public exploitation.
The patched versions, per Debian's own tracker: Bookworm's apt moved to 2.6.2 via DLA-4880-1, Trixie's to 3.0.4 via DSA-6607-1, and unstable to 3.3.6/3.3.7. Ubuntu shipped fixes the same day across 22.04 LTS, 24.04 LTS, 26.04 LTS, and 26.10. A standard apt update && apt upgrade on a current, supported release picks up the fix.
If you can't patch immediately, CSO Online's coverage reports Ubuntu's own guidance as twofold: temporarily set Acquire::Retries to 0 until you can update, which removes the precondition the flaw depends on entirely, and prefer HTTPS repository sources over plain HTTP where you have the choice, since tampering with HTTPS traffic in transit is a meaningfully harder position for an attacker to reach than tampering with plain HTTP. That second point is a mitigation, not a guarantee — a compromised mirror serving valid HTTPS, or an attacker who's otherwise gained a trusted position on the path, isn't fully ruled out by the protocol choice alone.
Why this is a fundamentals story for Linux administrators
Set the AI-assisted-discovery headline aside and what's left is a genuinely useful case study in how package manager trust actually breaks: not through a cracked signature or a stolen signing key, but through an interaction between two unrelated, individually reasonable features — redirect handling and download retries — that nobody had tested together under adversarial conditions. Knowing that a package manager's trust model has moving parts beyond "is the signature valid," and knowing which configuration settings widen or narrow your own exposure to a given class of bug, is exactly the kind of operational judgment that separates someone who runs apt upgrade on a schedule from someone who can actually reason about what that command is trusting and why. Innovative Academy's Linux Administration training in Bangalore covers package management on Debian and Red Hat-based systems in exactly this depth — not just the commands, but the underlying trust model, repository configuration, and the patch-management habits that mean an advisory like this one gets acted on by policy rather than by whoever happens to read the headline first. Contact for course details: 8447712333.
What we're not claiming
Neither Debian's advisory nor Ubuntu's own notice states that this flaw has been exploited in the wild — the "zero-day" language in circulation traces to Justicz's own informal description of his finding, not to a confirmed-exploitation classification from either vendor. His "any server running stock Ubuntu" framing is likewise his own characterization in a social media post rather than an independent risk assessment, and it understates the actual precondition: an attacker specifically needs on-path network positioning, which is a real but considerably narrower bar than it implies. We're relying on Debian's tracker entry and CSO Online's reporting for the mechanism described here rather than quoting Debian's full advisory text verbatim, since that document runs longer than can be reproduced directly — if you need the exact wording, DSA-6607-1 and DLA-4880-1 are the primary sources to check. Preferring HTTPS repositories reduces exposure but isn't presented here as a complete fix on its own, and older Debian or Ubuntu releases that predate the default-retries change aren't being described as immune outright — only as not exposed under their own default configuration.