
Oracle's October 2026 Patch Update Fixed 1,209 Flaws — Java SE Walked Away With Zero Critical Bugs for Once
1. Introduction
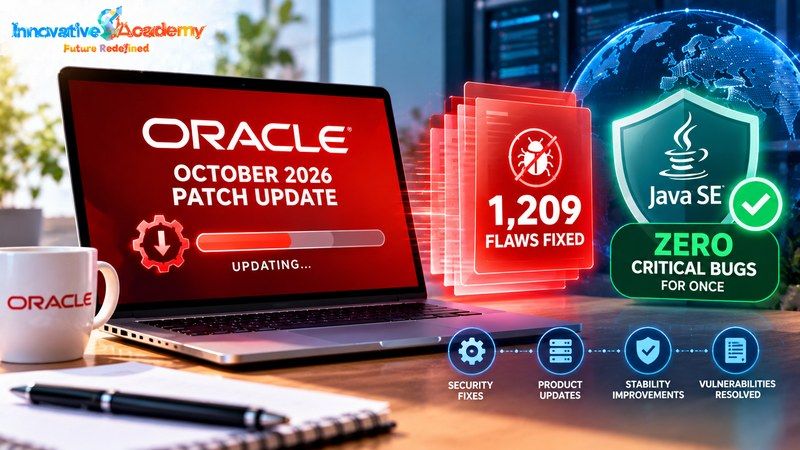
Oracle shipped its October 2026 Critical Patch Update on October 20, fixing 1,209 unique vulnerabilities across its entire product catalog, one of the largest quarterly security releases the company has put out. Buried inside that enormous number is a smaller, genuinely interesting detail for anyone working with Java: Java SE had no critical-severity flaws patched this quarter at all. That's worth sitting with for a moment rather than treating it as just another line in a routine patch cycle, because it's not the pattern Java SE's own patch history usually sets.
Target keywords: Java training Bangalore, Java course Bangalore, Oracle Critical Patch Update October 2026, Java SE vulnerabilities 2026, Oracle CPU October 2026, Java security patches, CVE Java SE 2026, Java certification Bangalore, Java developer training Bangalore, software security training Bangalore
2. The Scale of This Update
Oracle's Critical Patch Update process runs on a fixed quarterly schedule, January, April, July, and October, and this release landed 1,295 individual security patches addressing 1,209 unique CVEs across the full range of Oracle's software, from database and middleware products to applications like E-Business Suite and Oracle's various cloud offerings. That total places this among the heavier CPUs Oracle has issued in recent memory, a reminder that "patch Tuesday"-style release cycles aren't a Microsoft-only phenomenon, and that running any Oracle product means living on a predictable but genuinely substantial patching cadence.
3. Java SE's Report Card This Quarter
Out of that enormous total, 55 patches specifically address Java SE. The detail worth calling out directly: none of those 55 reach critical severity, and Java SE doesn't appear anywhere on this quarter's list of the most severe vulnerabilities across Oracle's product line. For a product that has historically been a recurring, sometimes heavily represented entry in past Oracle CPUs, a quarter with zero critical Java SE findings is a genuinely different outcome than business as usual, not a statement that Java SE is now flawless, but a specific, reportable fact about this particular release.
4. The Catch: "Not Critical" Doesn't Mean "Not Exploitable"
Here's where the headline number needs a second look rather than a sigh of relief. Of those same 55 Java SE patches, 49 address vulnerabilities that a remote attacker can exploit without supplying any credentials at all, no login, no valid session, no prior access to the system. Severity rating and exploitability aren't the same axis: a flaw can be rated below "critical" on Oracle's CVSS scale while still being trivially reachable by anyone who can send traffic to the affected service. Forty-nine out of fifty-five landing in that unauthenticated-exploit category paints a meaningfully different risk picture than "no criticals" alone suggests, and that ratio, not the absence of a critical label, is what ought to set how quickly a team books this update onto its patch calendar.
5. Why Java Keeps Showing Up in These Updates At All
Java SE's recurring presence in Oracle's CPUs isn't really a mystery once you consider what the platform is used for. It sits underneath an enormous share of enterprise backend systems, banking infrastructure, government platforms, and business applications that have been running continuously for years, often on top of libraries and dependencies that predate the current security landscape entirely. A security researcher finding a new way to exploit the JVM, a core library, or a long-standing API doesn't require Java to have gotten worse, it just requires enough attention from enough researchers over enough time, which is exactly what a platform this widely deployed attracts. Zero criticals this quarter doesn't change that underlying exposure; it just means this particular three-month window didn't surface one.
6. What This Means If You're Running Older Java Versions
Oracle's CPUs apply specifically to the Java versions still under Oracle's premier or extended support, which in practice means recent LTS releases like Java 21 and the newly current Java 25 line, plus whichever older LTS versions Oracle is still actively patching. If you're running a Java version that's already fallen out of Oracle's support window, these 55 patches, criticals or not, simply aren't being backported to what you're using. That's a distinct and arguably bigger risk than anything in this specific CPU: an unsupported Java runtime doesn't get safer by sitting still, it just stops getting told about its own problems.
7. What This Release Doesn't Tell You
This summary shouldn't be mistaken for the complete picture, and it's worth naming exactly what's missing: the source material for this piece didn't include the specific CVE identifiers behind the 55 Java SE patches, nor a breakdown of which Java components, the core JVM, specific libraries, or particular APIs, are actually affected. Whether any of these 49 unauthenticated-exploit flaws have already turned up in real attacks, rather than just being theoretically reachable, also isn't addressed anywhere in what's available here. Readers running Java in production are better served checking Oracle's own CPU advisory page directly for the exact CVE list and affected-version matrix than treating any secondary summary, this one included, as a substitute for it.
8. Java Fundamentals at Innovative Academy
Innovative Academy's Java Training program in Bangalore builds the practical, working knowledge of the JVM, core libraries, and application architecture that sits directly underneath exactly this kind of quarterly patch cycle, understanding what's actually running inside a Java application is what turns a CVE count in a security bulletin into something you can reason about rather than just a number to be anxious over.
9. FAQs
1. Does zero critical Java SE flaws this quarter mean Java is more secure than other Oracle products right now?
Not necessarily, and not in a way this release confirms either way. It means this specific CPU didn't surface a critical-severity Java SE finding, a fact about this one quarter's patch cycle, not a broader claim about Java's security standing relative to Oracle's other product lines.
2. If nothing is critical, why does this update still matter?
Because severity rating and exploitability are different measurements. 49 of the 55 Java SE patches this quarter fix flaws exploitable remotely without any credentials, a real risk factor independent of whether Oracle classified the underlying bug as critical.
3. How many total vulnerabilities did this October 2026 update address?
1,209 unique CVEs across Oracle's entire product catalog, via 1,295 individual security patches, making it one of Oracle's larger quarterly updates.
4. How often does Oracle release these Critical Patch Updates?
Quarterly, on a fixed schedule: January, April, July, and October.
5. Should I still apply these Java SE patches if none are rated critical?
Yes. The high share of unauthenticated-exploitable flaws among this quarter's 55 Java SE patches is itself a reason to patch promptly, regardless of the severity label attached to any individual CVE.
10. Final Thoughts
A quarter with no critical Java SE findings is a genuinely good data point, and it's worth taking at face value rather than assuming every Oracle CPU must be uniformly alarming. But the 49-out-of-55 unauthenticated-exploitability figure sitting right next to that good news is the part that actually determines how a team should prioritize this update, not the absence of a "critical" label. Reading a patch bulletin well means checking both numbers, not stopping at whichever one happens to sound more reassuring.