
Capcom Just Confirmed 11.7 Million Accounts Were Exposed — Here's What Actually Got Taken
Table of Contents
- Introduction
- What Capcom Actually Confirmed
- The Detail Worth Noticing: Most of the Damage Is Shallow
- The 196 Accounts Where Something Different Happened
- Why Email Addresses Alone Still Matter
- Reading This Against the Rest of October's Breach Wave
- What This Release Doesn't Tell You
- System and Account Security Fundamentals at Innovative Academy
- FAQs
- Final Thoughts
1. Introduction
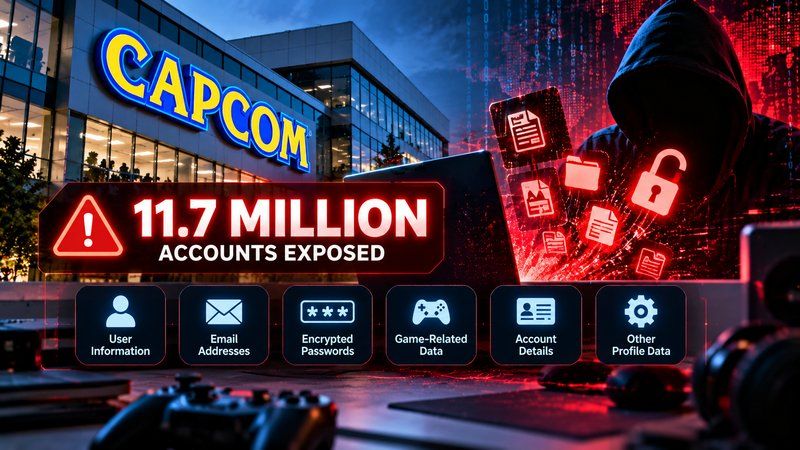
Capcom confirmed unauthorized access to its CAPCOM ID membership service on October 19, and the number attached to the disclosure, 11.7 million accounts, sounds like the kind of breach that should dominate a week's security news. Reading past the headline count to what was actually exposed tells a more specific and more useful story than the raw number alone, and it's worth separating what happened to most of those accounts from what happened to a much smaller group inside them.
2. What Capcom Actually Confirmed
Capcom detected suspicious activity against its CAPCOM ID membership service and confirmed unauthorized access on October 19. The confirmed scope: email addresses tied to 11.7 million CAPCOM ID accounts, along with account creation date, last login timestamp, and login count for each account, plus the IP address recorded at each account's most recent login. That's the baseline exposure across the full 11.7 million figure, metadata about accounts and contact information, rather than passwords, payment details, or government identifiers.
3. The Detail Worth Noticing: Most of the Damage Is Shallow
Here's the part of this disclosure that actually deserves attention rather than the headline number alone: for the overwhelming majority of the 11.7 million affected accounts, what leaked is contact and login metadata, not the kind of deeply sensitive personal data that shows up in breaches involving healthcare records, financial details, or government IDs. An email address paired with a login timestamp and an IP address is a real privacy exposure, useful for phishing and for building a profile of someone's online activity, but it's a different category of harm than a breach exposing passwords or payment card numbers outright.
4. The 196 Accounts Where Something Different Happened
Buried inside the 11.7 million figure is a much smaller, much more serious subset: for 196 accounts specifically, attackers changed the account passwords, directly locking the original owners out of their own CAPCOM ID. Capcom reset those accounts afterward. That's a meaningfully different category of compromise than exposed metadata, it means the attackers had enough access or control to actually take over a working authentication session or credential for those specific accounts, not just view data about them. For a small, separate group of 43 accounts, additional personal details, date of birth, gender, nickname, and country, were also exposed, a narrower but deeper breach sitting inside the much larger shallow one.
5. Why Email Addresses Alone Still Matter
It's tempting to read "just email addresses and login metadata" as a minor outcome, but that undersells the real risk. An email address confirmed to be actively associated with a specific gaming platform account is directly useful for targeted phishing, attackers now know which inboxes belong to real, active CAPCOM ID holders, and can craft messages that reference the platform specifically to improve their odds of a click. Login timestamps and IP addresses add enough context to make a phishing attempt look more credible, referencing a "recent login from an unfamiliar location" is a standard social-engineering tactic, and this breach handed attackers exactly the raw material that tactic needs.
6. Reading This Against the Rest of October's Breach Wave
Capcom's disclosure landed in the same general window as several other breaches reported this October, including incidents at Burger King Japan, Japanese financial media company Nikkei, and a developer hosting platform. Across that wave, the pattern worth noticing is how differently "breach" can mean different things: some incidents exposed deep, sensitive personal data for smaller groups, others exposed shallow contact metadata across enormous user bases. Capcom's disclosure sits closer to the second category for the bulk of its 11.7 million figure, with a sharper, more serious compromise concentrated in a much smaller slice.
7. What This Release Doesn't Tell You
Available reporting on this breach doesn't specify how the attackers originally gained access to the membership service, whether through a vulnerability in the platform itself, compromised employee credentials, or some other vector, and it doesn't say how long the unauthorized access persisted before detection on October 19. It also doesn't explain the specific technique used to change passwords on the 196 affected accounts, information that would clarify whether this was a targeted account-takeover campaign or an automated attempt that happened to succeed against a small subset.
8. System and Account Security Fundamentals at Innovative Academy
Innovative Academy doesn't run a dedicated cybersecurity program, but its Linux Administration training in Bangalore covers the account management, authentication configuration, and system-hardening fundamentals that sit directly underneath an incident like this one, understanding how user accounts, login logging, and access controls actually work at the system level is what separates reading a breach headline from understanding why 196 specific accounts ended up fully compromised while millions of others only had metadata exposed.
9. FAQs
1. Were passwords or payment details exposed in the Capcom breach?
Not for the bulk of the 11.7 million affected accounts. The confirmed exposure for that group is email addresses, account creation date, last login timestamp, login count, and the IP address at last login, not passwords or payment information.
2. Did any accounts get fully taken over?
Yes, for a small subset: attackers changed the passwords on 196 accounts, locking the original owners out before Capcom reset them.
3. Was any additional personal data exposed beyond contact and login metadata?
For 43 accounts specifically, yes: date of birth, gender, nickname, and country were also exposed, a narrower but more detailed compromise within the larger breach.
4. When did Capcom confirm this breach?
Capcom detected suspicious activity and confirmed unauthorized access to its CAPCOM ID membership service on October 19, 2026.
5. What should someone with a CAPCOM ID account do?
Available reporting doesn't give Capcom's specific guidance to affected users, but standard practice after a breach involving account metadata includes watching for phishing emails referencing the platform and enabling any available two-factor authentication on the account.
10. Final Thoughts
The honest read on Capcom's breach is that "11.7 million accounts" and "196 accounts" describe two genuinely different incidents sitting inside the same disclosure. The larger number represents a real but comparatively shallow exposure of contact and login data, useful mainly for phishing rather than direct account takeover. The smaller number represents an actual compromise serious enough that Capcom had to reset accounts directly. Treating the headline figure as the whole story misses the detail that actually explains how bad this breach was for the people it hit hardest.
Innovative Academy — Contact for course details: 8447712333
Website · Facebook · Instagram