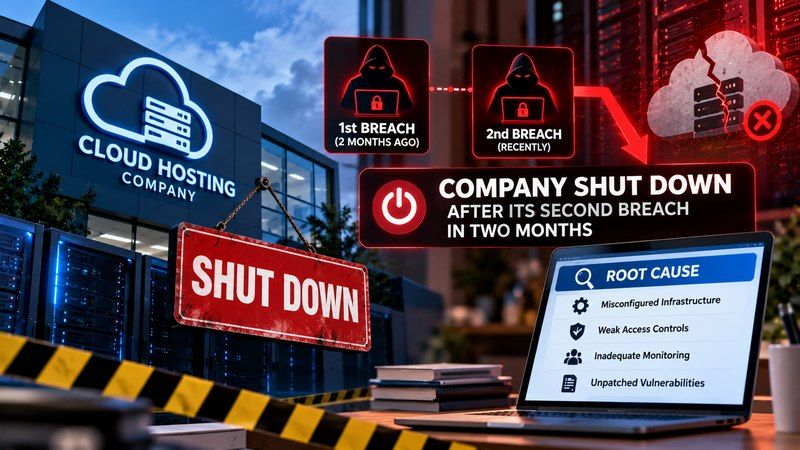

A Cloud Hosting Company Just Shut Down After Its Second Breach in Two Months — Here's the Root Cause
Table of Contents
- Introduction
- What Zeabur Actually Was
- The Root Cause, in Plain Terms
- What the Attackers Actually Did Once Inside
- The Numbers That Make This Different From a Routine Breach Disclosure
- Why "Second Breach in Two Months" Is the Real Story
- The Specific Mistakes a DevOps Practice Is Built to Prevent
- What This Release Doesn't Tell You
- Cloud and DevOps Fundamentals at Innovative Academy
- FAQs
- Final Thoughts
1. Introduction
Most data breach stories end with a company apologizing, offering credit monitoring, and moving on. Zeabur's doesn't. The developer cloud-hosting platform confirmed a second security breach in two months and announced it's shutting down entirely, services stop December 1, the company closes by December 31. That ending makes this worth reading past the headline count of exposed records, because the actual cause is a textbook case of exactly what credential-management and access-control practices are supposed to prevent.
2. What Zeabur Actually Was
Zeabur was a developer-focused cloud hosting platform, a Platform-as-a-Service product that let developers deploy applications without managing the underlying servers directly, the same general category as competitors like Render or Railway. That context matters for understanding the breach: a PaaS provider sits in a position of trust over every customer's environment variables, secrets, and deployed code, which is exactly why a security failure at this layer cascades across every customer running on the platform rather than staying contained to one account.
3. The Root Cause, in Plain Terms
According to reporting on the incident, the breach traces back to internal credentials that were stored in plaintext, unencrypted, readable by anyone who got access to wherever they were kept. That's not an exotic zero-day or a novel attack technique. It's one of the oldest, most preventable categories of security failure in software operations, and it's the first thing most credential-management training covers: secrets that unlock production infrastructure should never sit somewhere in a form that doesn't require a second layer of protection to read.
4. What the Attackers Actually Did Once Inside
Once the attackers had those credentials, the scale of what they could reach is the part worth sitting with. Zeabur confirmed root sign-ins on 101 Google Cloud Platform servers, carried out by 92 different user accounts. From there, the attackers added SSH keys to 50 of those servers, a move that plants a persistent way back in even if the original stolen credentials get rotated, and attached 16 customers' disk copies to virtual machines the attackers themselves controlled. That last detail is significant on its own: attaching a disk copy to an attacker-controlled VM is functionally equivalent to handing someone a full, readable copy of whatever was stored on that disk, without needing to compromise the running application at all.
5. The Numbers That Make This Different From a Routine Breach Disclosure
Over 3.2 million environment-variable records were exposed, along with account data for 321,810 users. Environment variables are where developers commonly store exactly the kind of sensitive material this breach otherwise shows the attackers hunting for: API keys, database passwords, third-party service tokens. A breach that exposes 3.2 million of those records isn't just a privacy incident, it's potentially a master key to a huge number of downstream systems that trusted Zeabur's customers, which is a meaningfully larger blast radius than a typical breach involving names and email addresses alone.
6. Why "Second Breach in Two Months" Is the Real Story
This is Zeabur's second confirmed security breach within a two-month span, and that detail changes how this incident should be read. A single breach, however bad, can happen to a well-run organization that gets unlucky once. A second breach inside two months, especially one rooted in something as basic as plaintext credential storage, suggests the first incident didn't trigger the kind of fundamental remediation that would have caught this. The shutdown decision reads less like an overreaction to one bad event and more like a company recognizing it couldn't rebuild customer trust after a pattern had already been established.
7. The Specific Mistakes a DevOps Practice Is Built to Prevent
Lay the pieces of this incident next to each other and they map almost exactly onto a standard DevOps and cloud-security checklist: credentials that belong in a dedicated secrets manager, not plaintext storage anywhere in the infrastructure; least-privilege access so that a single compromised credential doesn't grant root across 101 servers; monitoring that flags anomalous root sign-ins from 92 distinct accounts in a way that triggers an alert rather than going unnoticed; and controls on disk-snapshot attachment so that copying a customer's disk to an arbitrary VM isn't something a compromised credential alone can accomplish. None of these are advanced or unusual practices. They're the baseline a functioning DevOps and cloud-operations discipline is specifically designed to enforce.
8. What This Release Doesn't Tell You
The reporting available on this incident doesn't specify exactly how the plaintext credentials were originally obtained, whether through a prior breach, an insider, a misconfigured storage location, or something else, nor does it give a precise date for when the second breach actually began versus when it was detected. It also doesn't detail what, if anything, changed in Zeabur's security posture between the first breach two months earlier and this second one, which is the exact question that would explain whether this was preventable with the lessons already on the table.
9. Cloud and DevOps Fundamentals at Innovative Academy
Innovative Academy's DevOps Bootcamp in Bangalore covers exactly the secrets management, access control, and infrastructure-monitoring practices that this incident shows missing, the hands-on discipline of handling credentials, provisioning cloud access, and setting up the monitoring that turns an anomalous root login into a caught incident rather than a second breach two months later.
10. FAQs
1. What was Zeabur?
A developer-focused Platform-as-a-Service cloud hosting company, letting developers deploy applications without directly managing the underlying servers, in the same category as providers like Render or Railway.
2. What caused the breach?
Reporting on the incident points to internal credentials stored in plaintext, unencrypted, as the root cause, a basic and preventable credential-management failure rather than a novel attack technique.
3. How much access did the attackers actually get?
Confirmed root sign-ins on 101 Google Cloud Platform servers across 92 user accounts, SSH keys added to 50 servers for persistent access, and 16 customers' disk copies attached to attacker-controlled virtual machines.
4. How many records or accounts were exposed?
Over 3.2 million environment-variable records and account data for 321,810 users.
5. Why is Zeabur shutting down instead of just fixing the problem?
This was the company's second confirmed breach within two months. Services stop December 1, 2026, with the company fully closing by December 31, 2026, a decision that suggests the scale of the repeat failure outweighed what a straightforward fix could repair.
11. Final Thoughts
The uncomfortable lesson in Zeabur's breach isn't that attackers found something clever, it's that they didn't need to. Plaintext credentials, once found, opened a door to root access across more than a hundred servers, and from there the rest of the damage followed in a fairly predictable sequence. The practices that would have stopped this at multiple separate points, secrets management, least-privilege access, anomaly monitoring, aren't advanced techniques reserved for large enterprises. They're the baseline, and a company's inability to hold that baseline twice in two months is what actually closed it down.
Innovative Academy — Contact for course details: 8447712333
Website · Facebook · Instagram