
When the System Guarding Your Network Becomes the Target: Inside Cisco's Perfect-10 ISE Flaw
Table of Contents
- Introduction
- What Happened
- Why ISE Being the Target Matters So Much
- Inside the Vulnerability
- How It Surfaced
- Who's Affected, and the Fix
- Why "No Workaround" Changes the Calculus
- The Federal Deadline Angle
- The Actual Lesson Here
- Building This Skill Set in Bangalore
- Conclusion
- FAQs
1. Introduction
CVSS scores rarely hit the maximum. A 10.0 out of 10 means every dimension of the scoring—how easy the attack is to pull off, how little access the attacker needs, and how much damage it does—landed at the worst possible value simultaneously. Cisco handed out exactly that score in mid-September 2026 for a flaw in Identity Services Engine (ISE), the platform many enterprise networks trust to decide who and what gets network access in the first place.
For anyone studying networking or network security, this one is worth reading past the headline. It shows what "critical" looks like once you get past the label and into what an attacker can actually do.
2. What Happened
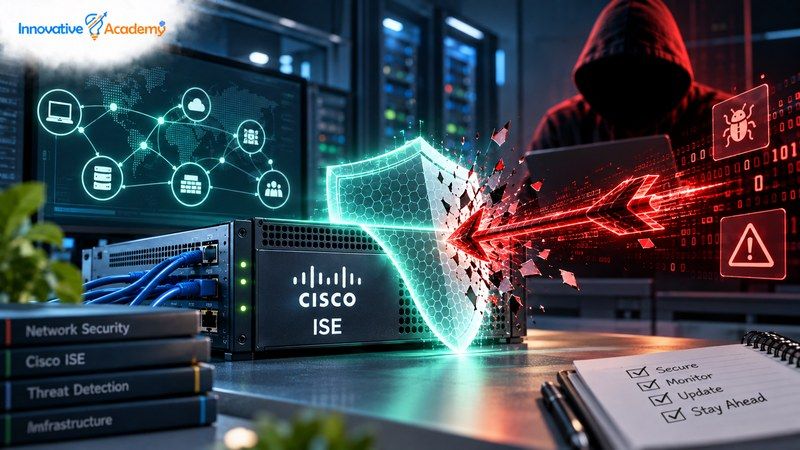
Cisco published a security advisory disclosing CVE-2026-76460, an authentication bypass vulnerability in Identity Services Engine (ISE) and ISE-PIC. Cisco also confirmed in the advisory that the vulnerability was already being actively exploited before the patch shipped, making it a genuine zero-day in practical terms.
Cisco rated the vulnerability CVSS 3.1 10.0, meaning every scoring dimension measured by the framework reached its most severe possible reading.
3. Why ISE Being the Target Matters So Much
Identity Services Engine isn't a peripheral add-on somewhere off to the side of a network. It acts as a gatekeeper that helps determine, in real time, whether a particular device or user receives network access.
ISE centralizes 802.1X authentication, profiles devices as they connect, checks posture before granting access, handles guest and BYOD onboarding, and pushes access policy to switches, wireless controllers, and firewalls, typically through RADIUS, TACACS+, or Cisco's pxGrid framework.
That's precisely why ISE is relevant to networking and network security coursework. Understanding ISE means understanding how "who's allowed on this network" is actually enforced, rather than simply seeing access control represented in a network diagram.
A flaw that gives an attacker administrative control over the system responsible for these decisions doesn't simply threaten one server. It can threaten the access-control layer for everything connected to the environment.
4. Inside the Vulnerability
The root issue is insufficient authentication validation on an API endpoint. This allows an unauthenticated, remote attacker to bypass ISE's web-based management interface entirely, without credentials, user interaction, or prior access.
The CVSS vector Cisco published—AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H—explains why the score reached 10.0. The vulnerability is network-reachable, has low attack complexity, requires no privileges or user interaction, has changed scope, and can have high impacts on confidentiality, integrity, and availability.
In plain terms, someone who can reach the ISE management interface could potentially obtain complete administrative control without successfully authenticating.
5. How It Surfaced
Cisco's advisory states that the vulnerability was discovered during the resolution of a customer's TAC support case rather than through a coordinated researcher disclosure or bug bounty submission.
Cisco's PSIRT language also confirms that active exploitation was occurring, although the advisory does not provide detailed information about attacker infrastructure or specific exploitation techniques.
More granular detection information, including specific log strings identified by some security researchers and vendors, comes from independent security analysis rather than Cisco's primary advisory. Such information should therefore be treated as supplementary rather than official Cisco guidance.
6. Who's Affected, and the Fix
ISE and ISE-PIC versions 3.1 through 3.5 are affected. Cisco has released fixed versions for each affected branch:
- ISE 3.1 Patch 12
- ISE 3.2 Patch 11
- ISE 3.3 Patch 12
- ISE 3.4 Patch 7
- ISE 3.5 Patch 4
Version 3.0 has already reached end-of-maintenance. Organizations still running it need to migrate to a supported release rather than wait for a patch that is not coming.
7. Why "No Workaround" Changes the Calculus
Cisco's advisory states plainly that there is no workaround for this vulnerability. Patching is the fix.
That's materially different from vulnerabilities where a firewall rule or temporary access restriction can buy security teams additional time. Some organizations may apply infrastructure ACLs to restrict who can reach the ISE management plane as a general defense-in-depth measure, but that should not be confused with an official Cisco mitigation that replaces patching.
If you administer ISE, the practical takeaway is simple: the patch should not be treated as optional maintenance to complete later. It is the primary remediation Cisco provides for the vulnerability.
8. The Federal Deadline Angle
Multiple security vendors and vulnerability trackers reported that CISA added the vulnerability to its Known Exploited Vulnerabilities (KEV) catalog around September 16, 2026. Those reports also cited September 19, 2026 as the remediation deadline for U.S. federal civilian agencies under the applicable binding operational directive process.
That specific deadline should be treated carefully because the date cited here comes from security vendor reporting rather than a direct verification of the CISA catalog for this article.
What is unambiguous is Cisco's confirmation of active exploitation. That alone makes the vulnerability significant for organizations operating affected ISE versions, regardless of whether a particular regulatory deadline applies to them.
9. The Actual Lesson Here
Strip away the specific CVE number, and this incident teaches something that repeatedly appears in real network operations: systems enforcing access control are themselves high-value targets.
Centralizing access enforcement is one of the reasons ISE is useful. However, that same centralization means a serious vulnerability in the platform can have an outsized impact on the surrounding network environment.
This incident also demonstrates why two facts need to be considered separately: active exploitation before public disclosure tells administrators how urgent the situation is, while the absence of a workaround tells them what remediation options are actually available.
Anyone building practical networking or network security skills should understand both aspects rather than focusing only on the CVE number or its CVSS score.
10. Building This Skill Set in Bangalore
Working through a scenario like this from the outside is useful. Being able to configure, secure, troubleshoot, and reason about networking and access-control technologies is what turns security knowledge into practical ability.
For learners looking to build these fundamentals, Innovative Academy's CCNA training program in Bangalore covers networking fundamentals, Cisco routing and switching, network security, automation, troubleshooting, advanced routing protocols, and network design, along with CCNA 200-301 exam preparation.
The program is designed around practical networking skills and includes hands-on work with Cisco equipment, networking projects, and a dedicated network security project. Training is available in classroom and online formats, with placement assistance for eligible students.
Learning concepts such as authentication, access control, routing, switching, network security, and troubleshooting provides a foundation for understanding real-world incidents such as vulnerabilities affecting enterprise network management platforms.
11. Conclusion
A CVSS 10.0 vulnerability affecting a system responsible for network access control is a serious security event. Cisco's confirmation of active exploitation before the patch was available adds further urgency.
For ISE administrators, the response is straightforward: upgrade to a fixed release because Cisco has confirmed that no workaround exists.
For anyone building toward a networking or network security career, the broader lesson is structural. Understanding why identity and access-control systems are important, how they interact with the wider network, and how to secure and troubleshoot them is more valuable than simply memorizing a CVE number.
12. FAQs
1. Is this vulnerability something only large enterprises running ISE need to worry about?
If you administer Cisco ISE at any scale, the vulnerability applies directly to your environment because the flaw is remotely exploitable without authentication. For students and early-career engineers, the broader lesson is understanding why centralized access-control platforms are high-value components of enterprise networks.
2. What should someone do if they're running an affected ISE version right now?
Apply the patched release for the relevant version as soon as possible: 3.1 Patch 12, 3.2 Patch 11, 3.3 Patch 12, 3.4 Patch 7, or 3.5 Patch 4. Cisco has stated that there is no workaround. Organizations running version 3.0 need to migrate to a supported release.
3. Is there hands-on Cisco networking and security training available in Bangalore, not just theory?
Innovative Academy offers CCNA-focused networking training in Bangalore with practical Cisco networking work, network security projects, CCNA 200-301 preparation, and placement assistance. The program is available through classroom and online learning formats.