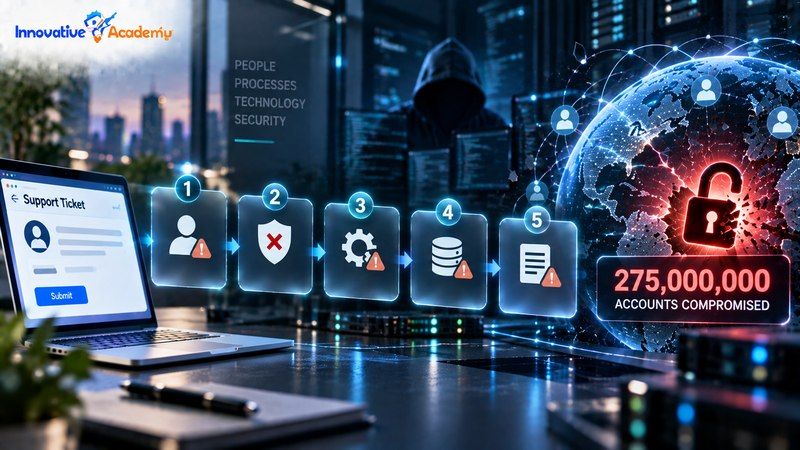

Five Mistakes That Turned One Support Ticket Into a 275-Million-Account Breach
Table of Contents
- 1. The Short Version
- 2. Mistake One: Trusting Rendered Content Without Sanitizing It
- 3. Mistake Two: Letting a Support Session Reach Too Far
- 4. Mistake Three: A Second Flaw That Should Never Have Reached Production
- 5. Mistake Four: Missing the Quiet Middle of the Attack
- 6. Mistake Five: Underestimating What "Low-Value" Data Is Worth Together
- 7. What Good Practice Actually Looks Like
- 8. FAQs
1. The Short Version
Canvas, the learning management system used by schools and universities worldwide, suffered one of the largest reported education-sector breaches on record in 2026. Reports described approximately 275 million student accounts across 8,809 institutions, 3.65 terabytes of data taken, and a reported $10 million ransom paid to attackers tracked as ShinyHunters.
What makes this incident worth studying isn't an exotic technique that nobody could have anticipated. It is the combination of several ordinary security weaknesses that compounded into a much larger incident.
The reported sequence highlights five important security lessons: unsafe handling of rendered content, excessive access within a support session, a second XSS vulnerability, insufficient detection of slow-moving activity, and an underestimation of the value of seemingly non-financial data when collected at enormous scale.
2. Mistake One: Trusting Rendered Content Without Sanitizing It
The reported entry point was a support ticket submitted on April 22, 2026, with an attachment that allegedly contained hidden code. Reports have described the payload as being associated with content rendered through Canvas's DocViewer functionality.
Document-preview systems are designed to make files convenient to inspect inside a browser. However, any application that renders content supplied by users must treat that content as potentially hostile. If active content is not properly sanitized or isolated, an attacker may be able to execute code in the context of the application.
This is closely related to stored cross-site scripting (XSS), a long-established web application security vulnerability. In a stored XSS scenario, malicious content is saved by an application and subsequently executed when another user views the affected content.
The broader lesson is straightforward: attachments, comments, support tickets, previews, and other user-controlled content should never be trusted simply because they are displayed through a convenience feature.
3. Mistake Two: Letting a Support Session Reach Too Far
According to reports about the incident, a Canvas support representative opened the affected ticket on April 25, after which the hidden payload executed within an already-authenticated browser session.
The attackers reportedly used the compromised session between April 28 and April 30 to access data through Canvas APIs. They also reportedly revoked their access afterward, helping keep the activity less obvious.
The important security issue is not simply that a support employee opened a malicious attachment. Opening tickets and reviewing customer-submitted files are normal support activities.
The deeper issue is access scope. A support account or session should have only the permissions necessary to perform its intended responsibilities. If compromising one support session provides a path to substantial sensitive data, the resulting blast radius can become much larger than the original compromise.
This is why the principles of least privilege, session isolation, access segmentation, and strong authorization controls are important in modern systems.
4. Mistake Three: A Second Flaw That Should Never Have Reached Production
Reports indicate that the attackers later exploited a second XSS vulnerability in Canvas's discussion functionality. This reportedly provided a route from the earlier foothold toward administrator-level access.
Administrator privileges can dramatically change the consequences of an application compromise. Instead of being limited to a particular account or support function, an attacker with administrative privileges may gain access to much broader application functionality and data.
The reported incident therefore illustrates the importance of testing privilege boundaries, not merely testing individual features in isolation.
Security reviews should specifically examine whether a vulnerability in one component can be chained with another weakness to cross an authorization boundary. Code review, penetration testing, application security testing, and privilege-boundary assessments can all help identify these types of weaknesses before attackers do.
5. Mistake Four: Missing the Quiet Middle of the Attack
One of the most important aspects of the reported timeline is the gap between the initial compromise and the later escalation.
The initial support-session compromise was reported on April 25. Data extraction reportedly occurred between April 28 and April 30, while the subsequent administrator-level escalation was reported on May 7.
This type of timeline demonstrates why security monitoring cannot focus exclusively on dramatic events such as repeated failed logins, sudden account takeovers, or extremely large downloads occurring within a few minutes.
Patient attackers can spread activity across multiple days. They may authenticate normally, access legitimate APIs, perform small actions, and attempt to remove evidence afterward.
Effective detection therefore needs to examine behavior over time. Security teams can combine authentication logs, API activity, privilege changes, data-access patterns, endpoint telemetry, and other signals to identify activity that looks unusual when viewed as a sequence rather than as isolated events.
6. Mistake Five: Underestimating What "Low-Value" Data Is Worth Together
The reported stolen information included data such as usernames, email addresses, course enrollment records, and in-product messages. This type of information may not appear as immediately valuable as payment-card information when viewed individually.
However, data sensitivity depends heavily on context, combination, and scale.
When information from hundreds of millions of accounts is combined with details about schools, courses, instructors, and communications, it can provide an extensive source of information for highly targeted social-engineering and phishing attempts.
For example, knowing a student's actual school, course, and instructor could allow an attacker to construct a message that appears considerably more credible than a generic phishing email.
The security lesson is that organizations should not automatically classify non-financial information as low risk. A dataset can become highly valuable to attackers when multiple seemingly ordinary data points are combined at scale.
7. What Good Practice Actually Looks Like
Put the reported security failures together and the defensive principles become clearer.
- Sanitize user-controlled content: Treat attachments, comments, previews, and other submitted content as potentially hostile before rendering them.
- Apply least privilege: Give support accounts and internal tools only the permissions required for their specific responsibilities.
- Test privilege boundaries: Look for attack chains that allow a low-privilege vulnerability to become an administrator-level compromise.
- Monitor behavior over time: Detect slow-moving activity by correlating events across days and weeks instead of focusing only on sudden anomalies.
- Assess data by context and scale: Consider how seemingly ordinary information can become valuable when combined with other records.
- Build layered security controls: Assume that individual controls can fail and design additional barriers to limit the resulting blast radius.
These principles do not depend on exotic technology. They are fundamental practices in application security, networking, identity management, and systems administration.
For learners building practical networking and cybersecurity foundations, CCNA training in Bangalore can provide a starting point for understanding networking concepts, access control, infrastructure, and security fundamentals. Innovative Academy also provides practical IT training designed around real-world technical skills.
8. FAQs
1. What exactly is stored cross-site scripting (XSS)?
Stored XSS is a web application vulnerability in which malicious content is stored by an application and later executed in another user's browser when that content is displayed. The stored payload could potentially exist in areas such as comments, support tickets, messages, or other user-controlled content.
2. Why did a breach that started with one employee's browser become so large?
The reported attack involved multiple stages. The initial compromise of a support session allegedly provided access to application functionality and data, while a separate vulnerability reportedly enabled further privilege escalation. This illustrates why limiting the permissions of individual sessions and enforcing strong authorization boundaries are essential.
3. Why is least privilege important in cybersecurity?
Least privilege limits an account, application, or process to only the access it needs. If that account is compromised, the attacker has fewer opportunities to access systems or data outside the account's intended role.
4. Can non-financial data really create a security risk?
Yes. Names, email addresses, school information, course details, instructor information, and messages can become useful for phishing, impersonation, and social engineering. The potential risk increases when large datasets allow attackers to combine many individual pieces of information.
5. Why should security teams monitor attacks over several days?
Not every intrusion produces an immediate, obvious anomaly. Attackers can move slowly, use legitimate application interfaces, make small changes, and attempt to hide their activity. Long-term behavioral monitoring and correlation can help identify patterns that individual alerts may miss.
6. Is this type of case study useful for cybersecurity beginners?
Yes. Real-world incidents can help beginners connect concepts such as XSS, authentication, authorization, least privilege, privilege escalation, API security, logging, monitoring, and data protection to an actual attack sequence.