
Citrix NetScaler's Third Zero-Day Wave of 2026—and This Time a Researcher Found Actual Malware on a Patched Honeypot
Table of Contents
- Introduction
- The Newest One: CVE-2026-88779
- What Makes This Disclosure Different: Malware Actually Found
- Rewind Two Weeks: CVE-2026-88771 and CVE-2026-88772
- Four More Flaws Fixed the Same Week, With Less Fanfare
- Why NetScaler Specifically Keeps Showing Up
- The Fix and the Deadline Attached to It
- What Patching Alone Doesn't Solve
- Learning Network Security at Innovative Academy
- FAQs
- Final Thoughts
1. Introduction
Citrix has now disclosed three separate waves of actively exploited NetScaler vulnerabilities within about a five-week span in 2026, and the most recent one came with a detail that moves it past routine patch-and-move-on territory: a security researcher found an actual malware binary running on a honeypot system that had already been patched.
That detail is worth sitting with before getting to the technical specifics, because it says something about how fast attackers are moving relative to how fast organizations are actually applying fixes.
2. The Newest One: CVE-2026-88779
The most recently disclosed flaw, CVE-2026-88779, carries a CVSS score of 8.7 and sits in how NetScaler ADC and NetScaler Gateway appliances handle SAML authentication specifically—it only affects deployments with SAML-based gateways or AAA (authentication, authorization, and accounting) functionality enabled.
It's a memory buffer flaw that was initially understood as causing denial-of-service conditions—crashing the authentication process rather than handing over control of it.
First reports surfaced as unexpected NetScaler reboots in late September. Citrix published a security notice acknowledging a "newly observed issue," and emergency patches followed on Sunday, October 4, 2026.
3. What Makes This Disclosure Different: Malware Actually Found
What moved this specific flaw from "denial-of-service bug" to something more serious is that administrators started noticing authentication requests containing crafted usernames that embedded shell commands—commands designed to download a payload from a specific external IP address, save it to the system, and execute it.
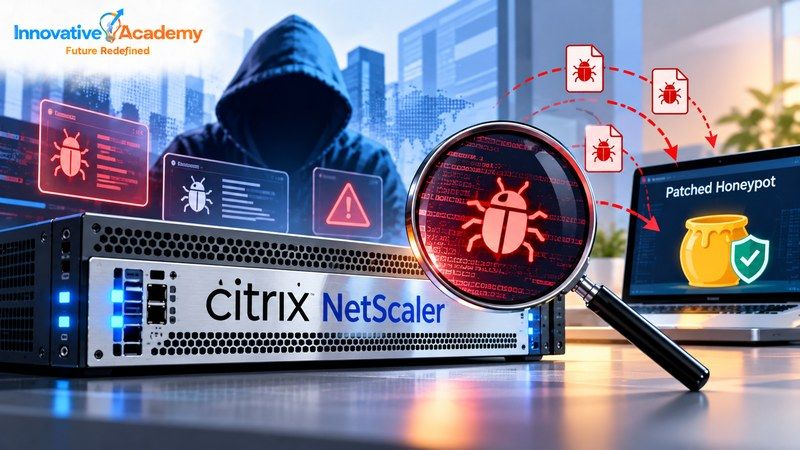
Independent security researcher Kevin Beaumont reported finding an actual downloaded malware binary running on a honeypot system he was monitoring, even after that system had already been patched against the vulnerability.
That suggests either the exploitation window before patching was wide enough to plant something persistent, or that the malware established itself through a path the initial patch didn't fully close. Either reading is uncomfortable, and both are reasons this disclosure is being treated as more than a routine DoS bug.
4. Rewind Two Weeks: CVE-2026-88771 and CVE-2026-88772
CVE-2026-88779 isn't NetScaler's first incident this cycle. Roughly two weeks earlier, Citrix disclosed CVE-2026-88771 and CVE-2026-88772, each rated 9.5 on the CVSS scale and, unlike the SAML flaw above, each capable of handing an attacker remote code execution rather than just crashing the authentication process.
- CVE-2026-88771 is an improper input validation flaw affecting all NetScaler deployments in their default configuration—no special feature needs to be enabled for a device to be vulnerable.
- CVE-2026-88772 is a separate memory overflow flaw specifically requiring DTLS (Datagram Transport Layer Security) to be enabled, exploitable through malformed DTLS traffic.
Exploitation of CVE-2026-88772 reportedly began by early September 2026, meaning attackers were actively using it for roughly three weeks before the public disclosure and patches arrived on September 27.
5. Four More Flaws Fixed the Same Week, With Less Fanfare
Alongside CVE-2026-88771 and CVE-2026-88772, Citrix's September 27 patch round quietly addressed four additional vulnerabilities—CVE-2026-88773 through CVE-2026-88778—ranging from CVSS 7.0 to 9.3 across various NetScaler configurations.
None of those four generated the same news coverage as the two actively exploited headline flaws patched alongside them, which is itself worth noting. A single patch release covering six distinct vulnerabilities, several of them rated high severity, is a reminder that the flaws that make headlines are often just the most urgent fraction of what actually needed fixing in any given release.
6. Why NetScaler Specifically Keeps Showing Up
NetScaler occupies the same structurally attractive position that's made other centralized network appliances—SD-WAN managers, VPN gateways—repeat targets throughout 2026: it sits at the network edge, handles authentication and traffic management for potentially thousands of users at once, and compromising it once can grant access disproportionate to the effort any single exploit required.
A flaw affecting SAML authentication specifically is particularly valuable precisely because SAML is how a huge number of organizations hand off trust to NetScaler in the first place. Break the thing that's supposed to verify who's allowed in, and the rest of whatever security the organization has built on top of that trust becomes considerably less reliable.
7. The Fix and the Deadline Attached to It
Citrix has released patched versions addressing CVE-2026-88779:
- NetScaler ADC and Gateway 14.1-73.41
- NetScaler ADC and Gateway 13.1-64.28
- Corresponding FIPS-compliant builds
Critically, Citrix has noted that organizations that already patched against the earlier September vulnerabilities (CVE-2026-88771/88772) still need to apply this separate, newer update—patching once this cycle doesn't cover the SAML-specific flaw disclosed afterward.
CISA logged CVE-2026-88779 into its Known Exploited Vulnerabilities list on October 4, 2026, giving federal civilian agencies only until October 7 to remediate—a notably compressed window, which tracks with how much weight the confirmed exploitation and Beaumont's malware finding have carried in how urgently this one is being treated.
8. What Patching Alone Doesn't Solve
Given that malware was reportedly found running on an already-patched honeypot, the practical lesson here extends past "apply the update."
Organizations that were running a vulnerable, internet-facing NetScaler appliance before October 4 should treat patching as the start of an investigation, not the end of one:
- Check authentication logs for the crafted-username pattern researchers have already documented.
- Review whether any unexpected files or processes appeared on the appliance during the exposure window.
- Don't assume a clean patch automatically means a clean system if exploitation may have already succeeded beforehand.
9. Learning Network Security at Innovative Academy
Innovative Academy's CCNA and CCNP programs in Bangalore get students hands-on with real networking gear and the authentication concepts—SAML trust relationships specifically among them—that sit at the center of a disclosure like this one.
Treating patching and post-incident investigation as two separate jobs rather than one finished task is exactly the kind of distinction that training is built to make second nature.
10. FAQs
1. Is the SAML flaw a different bug from the two Citrix fixed back in September?
Yes—CVE-2026-88779 is a distinct, newer flaw disclosed in early October, specifically affecting SAML-configured deployments. CVE-2026-88771 and CVE-2026-88772, patched in late September, are separate remote-code-execution flaws affecting different configurations.
2. If I already patched against the September NetScaler vulnerabilities, am I protected against this one too?
No—Citrix has specifically noted that the September patches don't cover CVE-2026-88779, so a separate update needs to be applied even on systems that were already patched against the earlier flaws.
3. Is this vulnerability only a denial-of-service issue, or something worse?
It was initially characterized as denial-of-service, but researchers have since documented evidence—crafted authentication requests and an actual malware binary found on a patched honeypot—suggesting the real-world impact may extend to remote code execution in at least some cases.
4. How many separate NetScaler zero-days does this incident make in 2026?
This incident is the third distinct wave within roughly five weeks: CVE-2026-88771 and CVE-2026-88772 in late September, and CVE-2026-88779 in early October, plus four additional lower-profile flaws patched alongside the September pair.
5. What should an organization do if it finds evidence of the crafted-username pattern in its authentication logs?
Treat it as a likely compromise rather than a false alarm—patching the vulnerability closes the hole going forward but doesn't remove anything that may have already been planted on the system, which requires separate investigation and incident response.
11. Final Thoughts
Three NetScaler zero-day waves in roughly five weeks, with the most recent one confirmed to include actual malware found on a patched system, is a pattern that outgrows any single CVE number.
It's a reminder that for infrastructure sitting at the network edge handling authentication for thousands of users, patching speed and incident investigation both matter—and that the gap between "exploited" and "patched" is exactly where the attackers behind Beaumont's honeypot finding seem to have been operating.
Want to build hands-on network security skills? Explore the networking and security training programs at Innovative Academy and learn the fundamentals that matter when edge infrastructure is under attack.
Sources
- Bleeping Computer — Citrix patches NetScaler SAML zero-day exploited in attacks
- Tenable — Frequently Asked Questions About Reported Citrix NetScaler Zero-Day Vulnerabilities
- Innovative Academy — CCNA Training in Bangalore