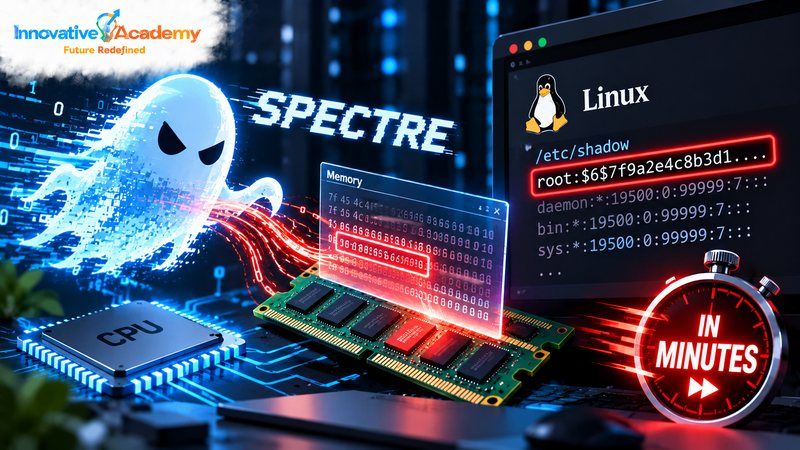

A New Spectre Variant Can Pull a Linux Root Password Hash Out of Memory in Minutes
Table of Contents
- Introduction
- What Researchers Actually Found
- How Branch Target Reuse Actually Works
- How the Root Password Hash Leak Actually Happened
- What a "Leaked Hash" Does and Doesn't Mean
- Why This Isn't Really an Intel-Only Problem
- The Patch Exists, But Most Systems Don't Have It Yet
- Why Shared Hosting and Multi-Tenant Servers Should Worry About This First
- What This Teaches About CPU Security Eight Years After the Original Spectre
- Building This Foundation at Innovative Academy
- FAQs
- Final Thoughts
1. Introduction
Eight years after Spectre first taught the industry that a CPU's own performance optimizations could be turned into a data leak, researchers have disclosed a new variant that does something genuinely striking: recover a Linux system's root password hash directly out of memory in a matter of minutes, using nothing more than an unprivileged process already running on the machine.
2. What Researchers Actually Found
The attack, named Branch Target Reuse (BTR), was disclosed on September 29, 2026 by researchers at VUsec, the systems and network security group at VU Amsterdam, working with Scuola Superiore Sant'Anna. It's formally tracked as two separate CVEs, CVE-2026-64507 and CVE-2026-64508, both affecting how the Linux kernel's BPF just-in-time compiler interacts with the CPU's branch predictor. It's a new variant within the Spectre v2 family, the same broad category of CPU speculative-execution flaw that's been a recurring theme in processor security since the original Spectre and Meltdown disclosures in January 2018. The researchers' core finding is that despite eight years of mitigations built specifically around this attack family, a new way through it still existed, unnoticed, until now.
3. How Branch Target Reuse Actually Works
Modern CPUs speed themselves up by predicting which direction a branch instruction will take and speculatively executing code down that predicted path before confirming that it is correct, rolling back cleanly if the guess was wrong. BTR exploits a specific gap in how that prediction interacts with memory reuse: when a JIT compiler frees a piece of compiled code and later places new code at that same memory address, the branch predictor can still be holding onto stale target information trained on the code that used to live there. In the researchers' Linux testing, an unprivileged classic BPF program trained the predictor, got freed, and a different program then got loaded into that same reused memory region. The CPU, still carrying the stale prediction, briefly and speculatively executed instructions at a misaligned offset that the new, legitimate program never actually intended to run. That misdirected speculative execution touched memory in a way that left a measurable trace in the CPU's cache, a trace precise enough to let the researchers reconstruct the underlying data one byte at a time.
4. How the Root Password Hash Leak Actually Happened
To demonstrate real-world impact rather than a purely theoretical primitive, the researchers pointed the technique at a running su process on the target Linux system and used it to recover the root account's password hash directly out of that process's memory, at a rate of roughly eight bytes of leaked data per second. Averaged end to end, that added up to about three minutes to fully recover the hash on Intel's Raptor Cove microarchitecture and about five minutes on Lion Cove. Those numbers make clear this isn't a slow, impractical side channel confined to a research paper; it's fast enough to matter on a real, live system.
5. What a "Leaked Hash" Does and Doesn't Mean
It's worth being precise here rather than letting the headline number do the explaining: recovering a password hash is not the same thing as recovering the plaintext password, and it doesn't hand an attacker root access by itself. What BTR actually provides, formally, is a way for a local, unprivileged user to read memory they shouldn't otherwise be able to see, which is serious on its own but requires an additional step, cracking the recovered hash offline, before it translates into an actual login. How long that second step takes, or whether it succeeds at all, depends entirely on the hashing algorithm in use and the underlying password's own strength; a weak password behind a fast hashing scheme could fall quickly, while a strong password behind a slow, modern hashing algorithm might never practically crack at all. The genuinely alarming part isn't that this guarantees root access; it's that it removes what used to be a meaningful barrier: needing elevated privilege just to read sensitive process memory in the first place.
6. Why This Isn't Really an Intel-Only Problem
The specific, publicly demonstrated exploit in this disclosure targets Intel's Raptor Cove and Lion Cove microarchitectures, which makes it tempting to file this away as an Intel-specific issue. The researchers themselves push back on that framing directly: they report confirming the same underlying stale-branch-predictor behavior across every CPU they tested, spanning Intel, AMD, and Arm, and attribute the root cause to a structural fact about how branch predictors work in general: no current CPU design keeps its branch predictor state synchronized with the actual code occupying a given memory address once that memory gets reused. That's a meaningfully different and more concerning claim than "one vendor has a bug." It suggests the specific proof-of-concept here is Intel-first simply because that's where the researchers demonstrated it fastest, not because the underlying architectural gap is unique to Intel silicon.
7. The Patch Exists, But Most Systems Don't Have It Yet
The fix for both CVEs has already been merged into the upstream Linux kernel, landing on July 25, 2026, well before this disclosure went public, and conceptually it's straightforward: CVE-2026-64508 adds a branch-predictor flush mechanism, and CVE-2026-64507 actually puts it to use on x86 systems by issuing a hardware barrier instruction whenever JIT-compiled memory gets reused. The complication is distribution lag: as of this disclosure, major enterprise Linux distributions, including Red Hat Enterprise Linux and its downstream rebuilds as well as Canonical's Ubuntu, had not yet shipped the fix in their own kernel packages, even though it had been sitting in the upstream kernel for months. That gap between "the fix exists" and "the fix has actually reached the system you're running" is precisely why security teams can't treat an upstream kernel merge as equivalent to being protected; the only thing that actually protects a given server is the specific kernel package installed on it.
8. Why Shared Hosting and Multi-Tenant Servers Should Worry About This First
The attack's core requirement, an unprivileged local process, makes multi-tenant and shared-hosting environments a meaningfully higher-priority concern than a typical single-purpose server. Security researchers tracking this flaw have pointed out directly that any local process capable of running attacker-controlled code, including something as mundane as a PHP worker process compromised through a vulnerable WordPress plugin, can carry out this attack, with no special access or existing foothold beyond that initial compromise required. That reframes BTR from "a CPU research curiosity" into a genuinely practical escalation path on exactly the kind of shared infrastructure where an initial low-privilege compromise is already a known, common first step for an attacker:
- Shared web hosts
- Container platforms running untrusted tenant code
- CI runners executing third-party code
9. What This Teaches About CPU Security Eight Years After the Original Spectre
The uncomfortable lesson in BTR isn't that Spectre-class vulnerabilities are still being found in 2026; that was always going to keep happening given how deeply speculative execution is baked into modern CPU design. It's that a structural assumption underneath memory reuse itself, that a predictor trained on old code can't meaningfully leak information about new code placed in the same spot, turned out to be wrong, and nobody had specifically gone looking for that particular gap until now. Eight years of accumulated Spectre mitigations solved the specific attack patterns researchers already knew to defend against; they didn't, and structurally couldn't, close a category of flaw nobody had yet described. That's less a criticism of the mitigation work that's already shipped and more an honest statement about the limits of defending against a vulnerability class that's defined by what a CPU's own performance optimizations do, rather than by any single specific implementation bug.
10. Building This Foundation at Innovative Academy
Innovative Academy's Linux Administration program in Bangalore, alongside its Hardware & Networking course, builds exactly the kind of foundation that makes a disclosure like this one legible rather than abstract: understanding what a kernel actually does when it applies a security patch, why a CPU's own performance features can become an attack surface, and why "the fix exists upstream" and "my server is actually protected" are two different claims that require checking which kernel package is installed.
11. FAQs
1. Does Branch Target Reuse give an attacker root access directly?
No. It lets a local, unprivileged process read memory it shouldn't be able to see, which the researchers used to recover a root password hash, not the plaintext password or an actual login. Turning that hash into working access still requires cracking it offline, which isn't guaranteed to succeed.
2. Is my server protected if I'm running a recent Linux kernel?
Only if your specific distribution has actually shipped the fix. The patch landed in the upstream Linux kernel on July 25, 2026, but as of this disclosure, major distributions, including RHEL-based systems and Ubuntu, had not yet released it in their kernel packages, so "recent" isn't the same as "patched" here.
3. Is this only a problem for Intel CPUs?
The specific, publicly demonstrated exploit targets Intel's Raptor Cove and Lion Cove microarchitectures, but the researchers report confirming the same underlying branch-predictor behavior across Intel, AMD, and Arm CPUs they tested and describe the root cause as a structural issue affecting branch predictor design generally, not an Intel-specific implementation bug.
4. Why should shared hosting providers be especially concerned about this issue?
Because the attack only requires an unprivileged local process, which means any compromised low-privilege foothold, including something like a hacked WordPress plugin running as a PHP worker, is potentially enough to attempt it. That makes multi-tenant environments running untrusted code a higher-priority concern than single-purpose dedicated servers.
5. What should a system administrator actually do right now?
Check whether your specific Linux distribution and kernel version have shipped fixes for CVE-2026-64507 and CVE-2026-64508 specifically. Don't assume a recent-looking kernel version means you're covered, and treat any unpatched system as exposed rather than trying to judge exposure from configuration alone, since the underlying condition is difficult to rule out without the actual patch in place.
12. Final Thoughts
Branch Target Reuse is a reminder that Spectre-class vulnerabilities aren't a closed chapter from 2018; they're an ongoing category defined by how deeply speculative execution is wired into modern CPU performance, and new ways through existing mitigations can still surface nearly a decade later. The practical takeaway for anyone actually responsible for running Linux systems isn't panic; it's specificity: know which CVEs apply, know whether your actual distribution has shipped the fix yet, and don't let a general sense that "Spectre stuff got patched years ago" substitute for checking the one detail that actually determines whether a given server is exposed.
Build Real Linux Skills
Want to understand Linux servers well enough to know when they're actually protected? Explore Linux Administration Training in Bangalore or Hardware & Networking Training in Bangalore at Innovative Academy, or call 8447712333 for course details.