
A Critical, Unpatched RCE Is Sitting Inside One of the AI Boom's Own Caching Layers
Table of Contents
- Introduction
- What LMCache Actually Is
- What CVE-2026-105192 Actually Is
- The One Setting That Decides Whether This Is Theoretical or Immediately Dangerous
- Why "No Fix Available" Is the Detail That Matters Most Here
- This Isn't an Isolated Mistake: The ShadowMQ Pattern
- What to Actually Do About It Right Now
- What This Teaches About Trusting Convenience in Production Code
- Learning Python the Way That Prevents This at Innovative Academy
- FAQs
- Final Thoughts
1. Introduction
Most of the security stories chasing headlines this year involve a vendor patching something after the fact, CISA adding it to a federal must-fix list, and a deadline attached. This one is different in a way that's genuinely more unsettling: a critical, remotely exploitable flaw in a piece of software quietly sitting underneath a lot of today's AI infrastructure, disclosed on October 7, 2026, with no fix available at all as of this writing.
2. What LMCache Actually Is
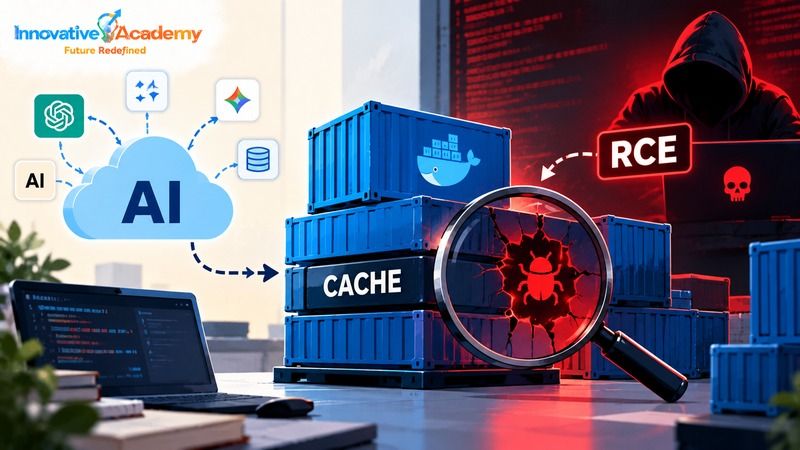
LMCache is open-source software built to make large language model serving faster, specifically by caching the intermediate computations (the "KV cache") that LLM inference engines like vLLM produce, so a model doesn't have to redo expensive work it's already done once. In its multiprocess mode, the cache runs as its own standalone server, and the various workers doing the actual model inference reach it over the network using ZeroMQ, a lightweight messaging library popular across the Python data and ML ecosystem for exactly this kind of inter-process communication. It's the kind of infrastructure plumbing that doesn't get much public attention precisely because it's working as intended most of the time, quietly making an LLM deployment faster without anyone outside the platform team needing to think about it.
3. What CVE-2026-105192 Actually Is
JFrog's security research team disclosed the flaw, tracked as CVE-2026-105192, on October 7, 2026, assigning it a severity score of 9.8 out of 10, squarely in the critical range. The root cause is a specific, well-known category of Python mistake: when LMCache's multiprocess server receives a message over its ZeroMQ socket, it unpacks that message's data using Python's pickle module before checking what type of object it's actually dealing with. Pickle wasn't designed to safely process data from an untrusted source; deserializing a crafted pickle payload can be made to execute arbitrary code as a side effect of simply loading it, and that's exactly the mechanism here. A single network message, with no login or credential of any kind, is enough to run commands as the user under which the LMCache process is running. The flaw affects LMCache versions 0.3.9 through 0.5.5, along with the 0.5.6 release candidates and the current development branch.
4. The One Setting That Decides Whether This Is Theoretical or Immediately Dangerous
Here's the detail that separates a flaw that's merely concerning from one that's actively dangerous in many real deployments: LMCache's multiprocess server only becomes reachable from across a network if an operator binds it to a routable address rather than leaving it on localhost, where it would only accept connections from the same machine. The trouble is that LMCache's own example Kubernetes deployment configuration binds the server to every available network interface by default, which is precisely the setting that turns this scenario from a flaw someone would have to go out of their way to expose into one that a lot of real-world clusters following the documented setup likely already have exposed. JFrog also flagged a second compounding factor: on LMCache's official container images, the process runs as root, meaning a successful exploit doesn't just run arbitrary code, it runs arbitrary code with full administrative privileges on that container.
5. Why "No Fix Available" Is the Detail That Matters Most Here
Every other major flaw covered in security news this year, including FortiMail, Citrix NetScaler, and Cisco's SD-WAN products, eventually got a vendor patch that organizations could actually apply. As of this disclosure, LMCache has not published a security advisory, and no fixed version exists. That leaves organizations running the affected versions with exactly one real option until a patch ships: reduce exposure through configuration rather than eliminate the vulnerability itself. JFrog's own guidance reflects that reality directly: keep the multiprocess server off routable network addresses entirely, restrict it to the local machine or a genuinely trusted cluster network, and understand that a firewall sitting in front of it lowers risk without actually removing it. The underlying code still has the flaw; it's just harder for an attacker to reach.
6. This Isn't an Isolated Mistake: The ShadowMQ Pattern
What makes CVE-2026-105192 worth more attention than a single unlucky bug in one project is that this exact mistake, pickle deserialization triggered by an incoming ZeroMQ message, has already shown up across a cluster of other AI inference frameworks under a pattern researchers named ShadowMQ: more than thirty related critical flaws found across projects, including Meta's Llama stack, NVIDIA's TensorRT-LLM, and other serving engines, traced back to the same unsafe code pattern spreading from one codebase to another through copy-paste and shared design conventions rather than each project independently making the identical mistake. LMCache fits squarely into that same lineage. The practical lesson isn't "this one library has a bug"; it's that an entire category of fast-moving AI infrastructure projects adopted the same convenient-but-unsafe shortcut at roughly the same time, which means anyone deploying AI inference infrastructure built in the last couple of years has a real reason to specifically check for this pattern rather than assuming it's confined to one unlucky project.
7. What to Actually Do About It Right Now
For anyone actually running LMCache in multiprocess mode today, the practical checklist is short but genuinely important:
- Check the bind address. Confirm the server isn't bound to a routable address. If it is, that's the single highest-priority fix available right now, regardless of whether a patch ever ships.
- Put a real network boundary in place. Use a trusted network boundary, not just a firewall rule assumed to be sufficient, between the cache server and anything outside the cluster that doesn't need to reach it.
- Don't run it as root. Avoid running the LMCache process as root where an alternative exists, since that single configuration choice is the difference between a contained compromise and a fully privileged one.
- Watch for the advisory. Keep an eye out for LMCache's own security advisory. A real fix, likely replacing the unsafe pickle-based deserialization with something that validates data before acting on it, is the only way this actually gets resolved rather than merely contained.
8. What This Teaches About Trusting Convenience in Production Code
Pickle's danger with untrusted input isn't a new or obscure fact; it's been documented in Python's own official library warnings for years. That's exactly what makes its reappearance here, in brand-new, fast-moving AI infrastructure, the more telling detail: a known hazard resurfacing in genuinely new code rather than a fresh discovery nobody could have anticipated. ZeroMQ's recv_pyobj()-style convenience methods, the ones that quietly deserialize incoming data with pickle on your behalf, are genuinely easy to reach for when you're building something quickly and the deployment is initially just a developer's own machine. The problem is that convenience methods chosen for an early prototype have a way of quietly surviving into production, in a library other projects then adopt wholesale, long after anyone's reconsidered whether the convenience was ever safe to begin with.
9. Learning Python the Way That Prevents This at Innovative Academy
Innovative Academy's Python program in Bangalore covers exactly this category of judgment alongside the language's syntax, not as an afterthought bolted onto the end of a course, but as part of learning what a given standard-library convenience actually does under the hood before reaching for it in real code. Understanding why pickle.loads() on untrusted data is fundamentally different from json.loads() on the same data isn't trivia; it's precisely the kind of foundational judgment that separates someone who can write Python that works from someone who can write Python that's safe to put in front of a network socket.
10. FAQs
1. Is my organization at risk from CVE-2026-105192?
Only if you're running LMCache's multiprocess mode. The real question to check immediately is whether that server is bound to a routable network address rather than localhost, since that's the specific condition that makes it remotely reachable at all.
2. Is there a patch available yet?
No. As of this disclosure, LMCache has not published a security advisory and no fixed version exists. The only available response right now is reducing exposure through network configuration, not eliminating the underlying flaw.
3. What's actually wrong with using pickle to deserialize data?
Pickle can execute arbitrary code as a side effect of deserializing a crafted object, which is fine when you control both ends of the communication completely but dangerous the moment any untrusted party can reach the socket accepting that data. It was never designed to safely parse data from a source you don't fully trust.
4. Is this related to other AI framework vulnerabilities covered this year?
Yes, directly. It fits the same pattern researchers named ShadowMQ: more than thirty related flaws across different AI inference projects, all traced back to the same unsafe pickle-over-ZeroMQ deserialization pattern spreading between codebases.
5. Does running the LMCache container as a non-root user fully fix the issue?
No, it limits the damage rather than closing the hole. The vulnerability itself, arbitrary code execution from a crafted network message, still exists either way. Running as a non-root user just means a successful exploit doesn't automatically carry full administrative privileges with it.
11. Final Thoughts
CVE-2026-105192 is a useful, if uncomfortable, reminder that the infrastructure holding up this year's AI boom is itself built out of ordinary code, written quickly, under real deployment pressure, by people reaching for the same convenient shortcuts developers have reached for for years. A pickle deserialization flaw is a textbook-old category of mistake showing up in brand-new software, with no patch yet available, sitting underneath systems a lot of organizations rushed to deploy. The fundamentals, understanding what your code is actually doing with data it didn't generate itself, matter just as much in 2026's AI infrastructure as they did in the Python codebases where this exact category of bug has been quietly breaking things for over a decade.
Learn Python the Right Way
Want to build Python skills that hold up in production, not just in tutorials? Explore Python Training in Bangalore at Innovative Academy or call 8447712333 for course details.